Let’s get technical
Here you will find information about architecture, specifications, documentation, APIs and more.
Learn more about RAC/M Identity
How RAC/M Identity works
A governance-first design centered on a single source of truth, wired to your systems through configuration rather than custom code.
Central identity repository
A central SQL repository of people, profiles, privileges and access levels, kept continuously in sync with connected systems, the single source of truth for who has access to what.
Identity Connector Framework (ICF)
A bidirectional connector layer that links the repository to identity sources, HR and ITSM systems, applications and databases, collecting access data and, on Premium, provisioning it back.
Configure, don’t code
The platform adapts to your technological and business context by configuring a rich array of built-in building blocks, eliminating costly customization and speeding deployment.
Deploy in SaaS mode or on prem
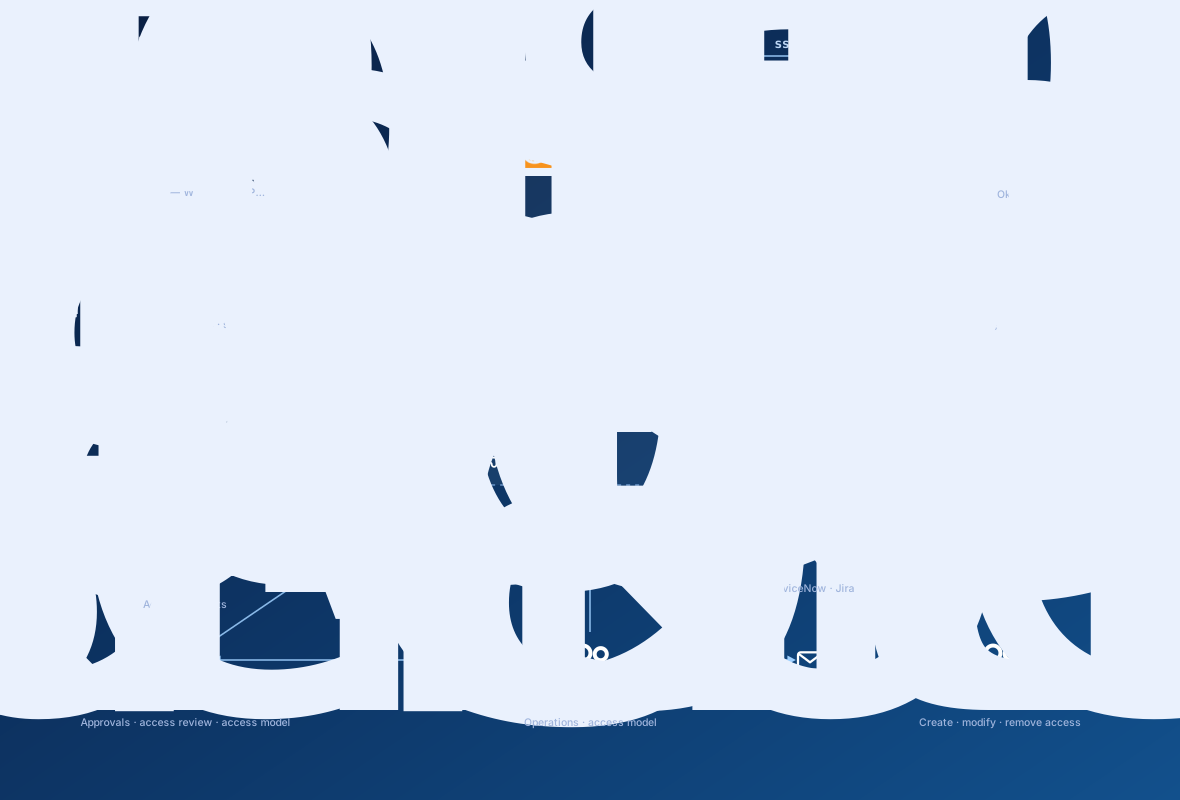
Three deployment options, distinguished by two responsibilities: who administers the platform, and who operates the governance program day to day.
On-premises
RAC/M Identity runs in your own infrastructure. You install, maintain and operate it end to end, backed by OKIOK’s proven methodology and support.
SaaS
OKIOK hosts and administers RAC/M Identity in a dedicated cloud tenant, with monitoring, patching, upgrading and evergreening, while you operate your own governance program.
Managed services
OKIOK both administers the platform and operates the governance program on your behalf, including access reviews, requests and the access model, as a turnkey service.
Automate everything, programmatically
A full REST API lets external systems such as ITSM platforms, AI agents and custom automations perform and manage IAM operations exactly as a human operator would, programmatically and at scale.
Beyond the API, the Identity Connector Framework (ICF) provides out-of-the-box, bidirectional connectivity to directories, HR and ITSM systems, SaaS applications and databases. Generic scripted, SCIM and JDBC connectors extend it to virtually any interface.
Secure by design, audited yearly
 Annual penetration testing
RAC/M Identity is designed from the ground up to be secure: strong encryption with TLS and Azure SQL, strong authentication via Entra ID or your preferred SAML IdP, and a hardened, dedicated tenant per customer.
Every change follows a formal change-management process with roll-back planning, audited annually under ISO 27001 and SOC 2 Type 2. The platform is tested by a professional offensive-security team through annual scans and penetration tests.
Platform, security & technical specifications
RAC/M Identity SaaS runs on Microsoft Azure, encrypted and monitored around the clock, on an extensible data model with broad, standards-based integration.
Platform & hostingRAC/M Identity SaaS only
- Cloud platform
- Microsoft Azure, dedicated per-customer tenant
- Network link to Azure tenant
- Point-to-point VPN or reverse-proxy agent (no inbound connections)
- Data residency
- Canada Central (Toronto) & Canada East (Quebec City)Other Azure regions determined by customers
- High availability
- Interzone geo-replication across regions
- Availability SLA
- 99.5% monthly, 24/7/365 · 99.99% High availability option available
Data & encryptionRAC/M Identity SaaS only
- Database
- Azure SQL
- Encryption at rest
- AES-256, Transparent Data Encryption (TDE)
- Encryption in motion
- TLS with recommended cipher suites
- Backups
- Azure SQL, 10-second resolution
- Disaster recovery
- RPO < 10 seconds, RTO < 4 hours
- Data retention
- 1 year by default, other duration available
Access & authentication
- Single Sign-On
- Entra ID / SAMLEntra ID SSO configuration →
- Multi-factor authentication (MFA)
- Leverages Entra ID or your IdP’s MFA mechanisms
- Password self-service
- Industry-standard PWM engine
Data model & scale
- Identities volume
- Unlimited
- Identities types
- Workforce, external, seasonal and other human identities, plus machines, bots, workloads and AI agents
- Account types
- Human, non-human, personal, privileged, service, shared, generic, technical
- Data model
- Dynamically extensible custom attributes
- Access models
- RBAC + ABAC + dynamic roles(role mining & modeling)
Integration & APIs
- Connectors
- ICF bidirectional connectorsAvailable connectors →
- Collectors
- Unidirectional flat files(CSV, XLS, XLSX, IDOC)
- APIs
- REST API for admin automationREST API reference →Manual provisioning API for customizing email requests and ticketsManual provisioning →
- API authentication
- OAuth 2.0
User interface
- Supported browsers
- Edge, Chrome, Firefox, Safari(Windows, macOS & iOS)
- Client access
- Any device with a compatible browser
- User interface
- Fully customizable look and feel
- Languages
- French and English, selected by locale, browser setting or user preference
- Notifications
- Fully customizable emails with MVEL scripts and manual provisioning API
Subscription
- Subscription
- Annual, based on the number of active identities
- Environments
- Includes a pre-production environmentAdditional environments available
Operations & support
- MonitoringRAC/M Identity SaaS only
- 24/7/365 (availability, performance, security)
- Technical support
- Level 2 & 3Extended business hours included in subscription24/7/365 support available
- Support languages
- English & French
Product documentation
Full technical documentation lives in the online product docs. A few good starting points:
Put your technical questions to our experts
Evaluating RAC/M Identity for your environment? Talk to our product experts about architecture, integrations, deployment, security or any other technical requirements you need to validate.
Prefer to continue exploring on your own? Browse the RAC/M Identity datasheet, white papers and other technical resources.