Let’s get
technical
The complete technical specifications for S-Filer Portal: encryption and protocols, authentication and identity, compliance, deployment and platform support.
Learn more about S-Filer Portal
Functional architecture
How S-Filer Portal fits into your environment, from your users to the storage, databases and directories behind it.
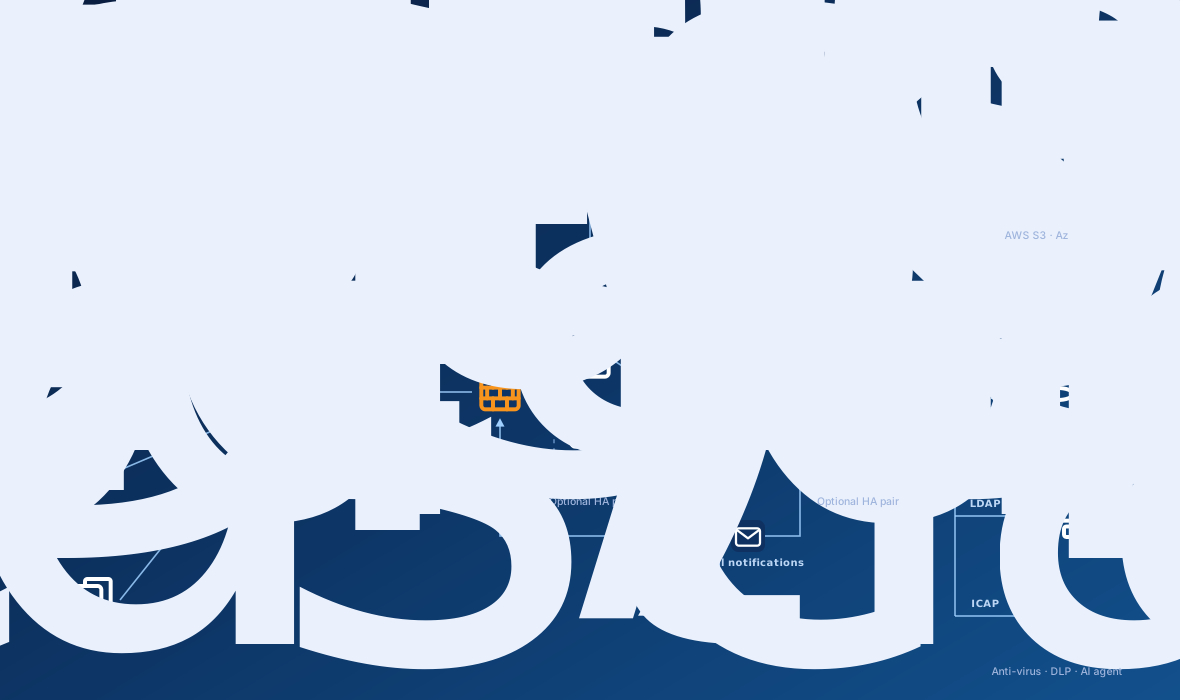
Deploy in SaaS mode or on prem
Two deployment models, distinguished by who administers the platform.
On-premises
S-Filer Portal runs in your own infrastructure: 1-, 2- or 3-tier, on Windows or Linux virtual machines or in Docker and Kubernetes containers, with your choice of database. You install, maintain and operate it end to end, backed by OKIOK’s proven methodology and support.
SaaS
OKIOK hosts and administers S-Filer Portal in a dedicated Microsoft Azure tenant, in your designated region, monitored, patched and upgraded, while you operate your own transfer service and manage your users. You get the full-featured platform with no infrastructure to provision, scale or maintain.
Deployment & operations
- 1-, 2- or 3-tier topology
- DMZ protocol gateway relaying FTP, FTPS and SFTP
- Load balancing and reverse proxy (Apache mod_proxy, IIS ARR)
- Modular server / gateway / CLI components on Windows and Linux
- In-place upgrades that preserve configuration
- Service integration and performance tuning (Java heap, timeouts, concurrency)
Automate everything, programmatically
A full REST API and a scriptable CLI let external systems, AI agents and custom automations perform and manage file-transfer operations exactly as a human operator would, programmatically and at scale.
Beyond the API, S-Filer Portal integrates out of the box with your directories, cloud and network storage, and databases, and connects to ICAP content-scanning services for anti-virus and DLP. Command-line tools and standards-based protocols extend it to virtually any system.
Secure by design, audited yearly
 Annual penetration testing
S-Filer Portal is designed from the ground up to be secure: files are encrypted at rest with AES-256 in secure virtual vaults, transfers are protected over TLS with optional end-to-end encryption, and strong authentication is handled by your preferred SAML or OpenID Connect identity provider.
Every change follows a formal change-management process with roll-back planning, audited annually under ISO 27001. An independent CPA firm examines the SaaS service over a full audit period and issues an annual SOC 2 Type 2 attestation. The platform is tested by a professional offensive-security team through annual scans and penetration tests.
Cryptography & key management
- Per-user and per-community RSA key pairs (2048/4096-bit)
- PKCS#7 key-envelope wrapping of per-file keys
- Built-in PKI / internal certificate authority
- Key rotation, revocation and re-encryption
- Transparent Data Encryption (TDE) for stored key material
- Obfuscated private-key storage with tightly controlled access
Web & session hardening
- HTTPS and HSTS enforcement
- Secure cookies
- Clickjacking (iFrame) protection
- Managed session cookies with inactivity timeout
- IP address allowlisting (CIDR ranges)
Audit & monitoring
- Per-category and per-event audit toggles, applied in real time
- Built-in integrity-check audit entries
- PDF and CSV export with date and event-type filtering
- SIEM forwarding via syslog (brute-force, exfiltration and mass-deletion use cases)
Specifications
Everything you need to evaluate, deploy and integrate S-Filer Portal.
Encryption & cryptography
- Encryption
- AES-256Recommended cipher suites
- Hashing
- SHA-256Recommended hashing algorithms
- Content protection
- S/MIME V3 and PKCS#7
- Certificates
- X.509 V3
- End-to-end encryption
- Optional
Protocols & transport
- Transfer protocols
- HTTPS, SFTP, FTPS, SCP, SSH
- Transport security
- HTTPS/SSL, TLS 1.2 and TLS 1.3
- Cryptography
- Digital signature & public-key based on recommended cipher suites
Authentication & identity
- Passwords
- Active Directory or local accounts
- SSO
- Kerberos, Active Directory, any SAML 2.0 IdP (Entra ID, Okta, Ping, ADFS, etc.), OpenID Connect
- Directory integration
- LDAP
- MFA
- RFC 6238 time-based OTP, email, SMS
- API authentication
- API Tokens
- SMTP authentication
- OAuth 2.0
Compliance
- Standards & regulations supported
- PCI DSSHIPAAQuebec Law 25Santé Québec TGVGDPRPIPEDA
SaaS deployment
- Cloud platform
- Dedicated Microsoft Azure tenant
- Data residency
- Customer-designated Azure region
- Database
- Azure SQL
On-premise deployment
- Architecture
- 1-, 2- or 3-tier with DMZ gateway
- Hosting
- Virtual machines, Docker and Kubernetes containers
- Operating systems
- Windows Server 2016 or laterLinux (all distributions)
- Databases
- MS SQL, Oracle, MySQL / MariaDB
Client support
- Web browsers
- Edge, Firefox, Chrome, Safari
- Mobile
- iOS and Android
- Mobile app
- S-Filer Sanctum (iOS / Android)
- Transfer clients
- Any HTTPS, SFTP, FTPS, SSH or SCP client
- Accessibility
- WCAG 2.1 AA
- Responsive design
- Adapts to any device, mobile to desktop
Management & scalability
- Administration
- Web-based console
- Policies
- Global, community and share scope
- Delegation
- Delegated user, group and community administration
- Scalability
- Virtually unlimited
Product documentation
Full technical documentation lives in the online product docs.
Put your technical questions to our experts
Evaluating S-Filer Portal for your environment? Talk to our product experts about architecture, integrations, deployment, security, automation or any other technical requirements you need to validate.
Prefer to continue exploring on your own? Browse the S-Filer Portal resources.